
Profile for evilham

- Display name
- Evilham
- Username
- @evilham@unchat.cat
- Role
- admin
About evilham
Fields
- Hamart
- @hamart
- Joined
- Posts
- 688
- Followed by
- 277
- Following
- 633
Stats


Torno a fer Big Tech-shaming de l'administració pública.
He tingut un petit desastre involucrant pèrdua de dades (mea culpa totalment).
Entre altres, he revocat el meu certificat digital, emès per l'AOC (Administració Oberta de Catalunya). No m'hi he fixat gaire en el procès, perquè realment és estressant tot plegat i vaig per feina.
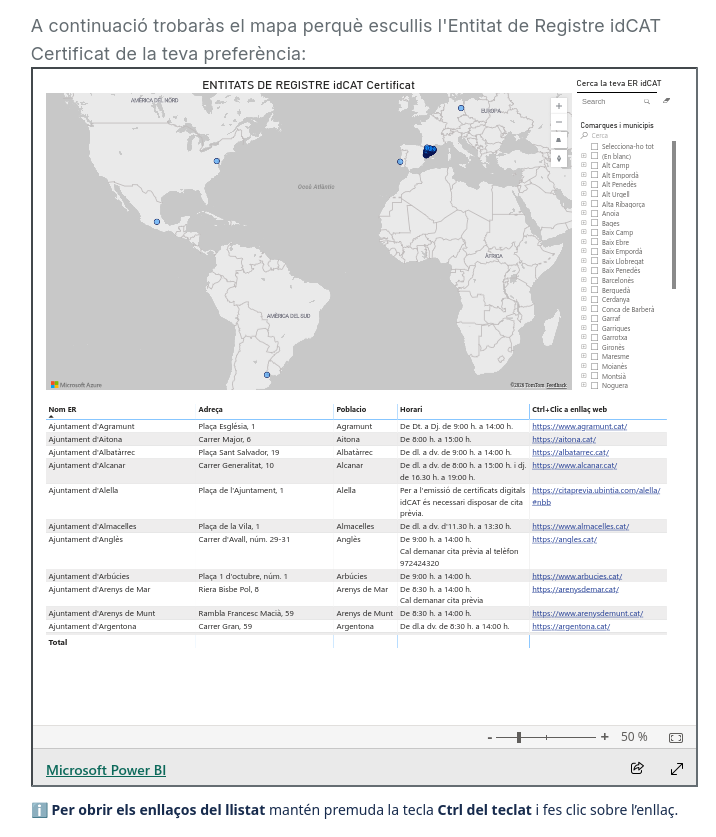
Però! Ara que vaig a demanar un certificat nou, em surt la llista de llocs on fer la comprovació d'identitat de la següent manera:
Un iframe del domini app.powerbi.com, un servei de Microsoft.
Ho podeu veure aquí: https://suport.aoc.cat/ca-ES/article/?servei=idcat-certificat&id=KA-07508_on-puc-obtenir-l-idcat-certificat
Sense cap tipus d'avís ni consentiment, em veig forçat a interactuar amb Microsoft, en un context en el que no només és totalment innecessari, sinó també inesperat.
https://fedi.unchat.cat/@evilham/statuses/01KEC42JGXZ7QZ9BW6X2ABKN5F
Since #FreeBSD people are already at #EuroBSDcon, here is a complain in the void (*):
It looks like the installer ignores the desire to encrypt the disk when using ZFS.
Realised this after setting up things and rebooting, and noticing "hey, it's not asking for the passphrase".
And, boy do I have some thoughts regarding bsdinstall zfsboot.
(*) haven't gotten the spoons yet for a proper bug report, but it will come once things are back to normal
TIL: a way to check a system's serial number (and other BIOS info):
# dmidecode -s baseboard-manufacturer
LENOVO
# dmidecode -s system-serial-number
XXXXXXXX
Pretty handy!
Estoy odiando el nic.es / red.es / dominios.es ahora mismo.
Diría que .es es el TLD más fastidioso de utilizar, absolutamente todo tiene que pasar por la plataforma increíblemente lenta de nic.es, donde cosas sencillas como "arreglar los datos de contacto" se convierten en un contrato que tienes que firmar 

Wrote a thing for #SysadminDay
Turns out, today has been one of those days that pass really quickly, without doing anything concrete, but actually doing many things. Just the geist of #SysadminAppreciationDay I guess.
Els fatxes de marca catalana tenen paradeta a Fabra i Puig, i els Mossos estan aparcats just al costat, no sigui que a algú no els agradi tenir-los al barri.
#FreeBSD question: I realised my laptop's hardware has a WWAN available, particularly: 0x1eac 0x1001, aka: EM120R-GL LTE Modem.
It looks like most of the right bits that would support this are in the system, but I can't seem to make it work (e.g. devctl won't forcefully attach the u3g driver).
Do I see correctly that rebuilding the u3g kernel module is the way to try this? I do see that QUECTEL has a vendor id of 0x2c7c, which is not what my pciconf is showing >,<
@bogo heeey, loved your talk, was checking a Matrix client you mentioned: Syphon, it looks like it hasn't had any activity for years or is easily installable nowadays. My guess is that since it hasn't kept up with changes in the ecosystem, things like file attachment wouldn't work.
Maybe you'll want to skip this one in the future :-D
See you next time!!!
Avui li toca a la Seguretat Social, que es veu que tinc una notificació, i tinc la targeta sanitària europea caducada, farem 2x1.
A veure què tal pinta interactuar amb la Seguretat Social :-)
https://fedi.unchat.cat/@evilham/statuses/01KEC42JGXZ7QZ9BW6X2ABKN5F
Segueixo amb el hobby de mirar coses ciutadanes, m'estic apalancant però he de "parlar" amb l'AEAT. Som-hi!
https://fedi.unchat.cat/@evilham/statuses/01KEC42JGXZ7QZ9BW6X2ABKN5F
So, fellow #email #selfhosting peeps.
What do we do about #Outlook? It used to be the case that we could follow a somewhat reasonable process to be unblocked by their bullshit policies.
(see: https://chaos.social/@evilham/109179040439027408 )
But nowadays that is not possible, and all we have is this stupid HTTP 500 with no real way of contacting them: https://substrate.office.com/ip-domain-management-snds/postmaster/troubleshooting#errors
I kinda want to send an email to a @hotmail.com human, whose only means of contact I have is email :-D.
Today's number is 1298.
Ehem @nico, I'm a monster, I know 
Estic flipant bastant amb que aquesta part tan important de l'administració depengui ambdós d'Amazon i Google, i que la ciutadania hagi de passar per aquí sí o sí
https://fedi.unchat.cat/@evilham/statuses/01KEC8CY0QPQ28T5E1J5X9ZE1F
Vinga, any nou, hobby nou:
Anem a documentar informalment la cessió de dades(*) forçada(**) per part les institucions públiques, durant la meva existència com a persona ciutadana a Barcelona.
(*): em concentraré en cessions de dades al règim autoritari dels Estats Units d'Amèrica, mitjançant les multinacionals que sotmeten les nostres institucions
(**): per "forçada" entendré: peticions automàtiques a servidors d'aquestes multinacionals, amb èmfasi en funcionalitats trencades quan aquestes peticions estan bloquejades
I had been maintaining a more privacy-friendly fork of an Android app, and released it on Google's Play Store.
It used to be mostly fine to deal with their paperwork and bureaucracy, nowadays it's ridiculous.
https://support.google.com/googleplay/android-developer/answer/13392821
They want app maintainers to upload a frigging video of each feature; this is SO MUCH added work for basically no gain. I could show just one place where these services are used in an OK fashion and not others where they could be shady.
Anyway, giving up on Google's crap and setting up a private #fdroid repository; that's significantly easier.

Gosh, I love how #FreeBSD makes some things so simple. Just deployed an #IPv6-only server, running a virtualised https://komo.do, for the various Linux-centric services that I might need.
Networking wasn't black magic but pretty straightforward, storage is safely backed by ZFS sparse zvols, and firewall is tight and simple with pf.
🥳 daily driver upgraded to #FreeBSD 15.0 with #pkgbase (was using it already since 13.X)
Besides the minor adjustments regarding changes to the names of #pkg repositories, which were announced on the mailing lists, everything went just as expected.
The fact that we now have a repository with kmod ports that match base is

Here is a tired ham asking for help from the #selfhosting #gemini fediverse.
I deployed gemserv to serve gemini://evilham.com "ages" ago, and for world political reasons I am step by step moving away from .com to .eu, which means I recently deployed gemini://evilham.eu.
So, the question:
How can I easily setup gemserv to redirect from evilham.com to evilham.eu, on all paths while not losing the paths?
I think the odds are thin, here is what the code says (the config is a HashMap<String, String>):
https://git.sr.ht/~int80h/gemserv/tree/827a9c148193b9726fbd9ffa4c1a02661b12ff7a/item/src/con_handler.rs#L169
Welp, I was going to migrate away from a pixelfed instance I have only to realise that ActivityPub Move was broken.
Luckily it looks like this got into the main branch recently, and will be in next release:
https://github.com/pixelfed/pixelfed/pull/6194/files
One final annoyance with my @gotosocial migration!
I implemented a split-domain setup, as wonderfully documented by @gotosocial here: docs.gotosocial.org/en/latest/
Note that #Mastodon also supports it, and documents it similarly here: docs.joinmastodon.org/admin/co
In both Mastodon and #GoToSocial, I notice that web clients FAIL to login with the account domain.
From what I see on the web server, the account domain receives exactly ONE request:
"POST /api/v1/apps HTTP/2.0" 404 146 "-" "Tusky/31.1 Android/15 OkHttp/5.1.0"
(This is Tusky, but Mastodon's app and others behave the same)
I tried to 301 / 307 redirect that endpoint (against @gotosocial's recommendation), but that fails in the same way (except I see the different matching code on the web server).
As a side effect, apps show my username as: at evilham at fedi.unchat.cat, instead of @evilham, which is what I actually wanted.
What to do? >,<